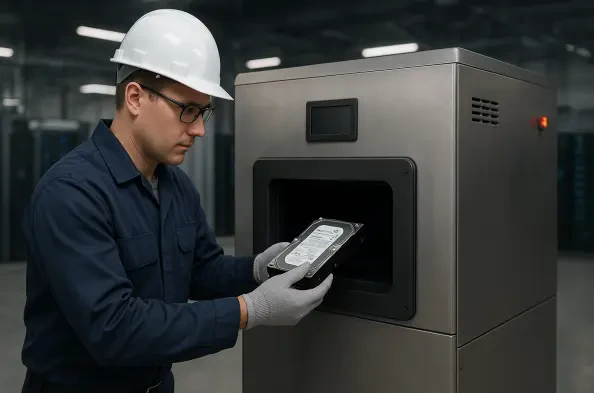
The common practice of storing retired laptops in unsecured closets creates a significant vulnerability that standard firewalls and password policies cannot address. Many organizations invest heavily in edge protection and sophisticated threat detection systems, yet they remain blind to the potential catastrophe sitting in their own storage rooms. This oversight stems from a pervasive belief that a device no longer in use is a device that no longer holds power. However, as digital footprints expand into every facet of corporate operations, the end-of-life stage for hardware has transformed into a primary vector for data exfiltration. In the current landscape of 2026, where data privacy regulations have become increasingly stringent, treating a decommissioned server as mere scrap is a gamble that few enterprises can afford to lose. The focus must shift from defending active networks to securing the entire lifecycle of every physical asset that has ever touched sensitive information.
The Gap Between Erasure and True Destruction
A profound misunderstanding exists regarding the permanence of digital information on retired storage media. Many IT managers rely on standard formatting or manual file deletion, assuming these actions render the data unrecoverable. In reality, these methods often only hide the files from the operating system while leaving the underlying binary data perfectly intact on the disk. Studies involving the purchase of used hard drives from public secondary markets consistently reveal a shocking trend: a high percentage of these devices still harbor sensitive corporate and personal information. From internal financial spreadsheets to private customer records, the residue left behind by insufficient sanitization provides a treasure trove for malicious actors. This gap between the perception of a clean drive and the technical reality of data persistence represents a massive, unaddressed liability that spans across industries from healthcare to global finance.
Understanding Data Residue and Regulatory Benchmarks
The failure of standard erasure methods is not merely a technical glitch but a fundamental structural flaw in how data is stored. When a user deletes a file, the computer essentially removes the entry from the table of contents, but the actual chapters of data remain on the physical disk until they are overwritten by new information. For retired devices that are simply turned off, that information remains indefinitely. Data recovery software, which has become increasingly accessible and user-friendly, allows almost anyone to scan a discarded drive and reconstruct entire directories of sensitive material. This risk is exacerbated in 2026 by the prevalence of solid-state drives, which handle data wear leveling in ways that can make traditional wiping methods even less effective. Without professional-grade overwriting or physical destruction, an organization’s most private secrets are essentially left on the sidewalk for the next passerby to claim.
Implementing National Media Sanitization Guidelines
To bridge this security gap, organizations are increasingly turning to the rigorous frameworks established by the National Institute of Standards and Technology. Specifically, the guidelines found in NIST SP 800-88 Rev. 2 have become the gold standard for media sanitization in 2026. This framework moves beyond simple deletion, detailing specific methods such as cryptographic erasure and physical destruction to ensure that data recovery is impossible even with forensic tools. For entities operating within highly regulated environments, adhering to these technical benchmarks is a non-negotiable component of their broader risk management strategy. By implementing a standardized approach to sanitization, a company ensures that every retired asset is handled with the same level of security scrutiny as a newly deployed server. This transition from informal disposal to a documented, technically sound process is essential for maintaining integrity and avoiding the legal consequences of a breach.
Professional Standards for IT Asset Disposition
Moving from technical sanitization to a comprehensive organizational strategy requires a shift toward professional IT Asset Disposition standards. A robust ITAD framework is built upon the dual pillars of technical destruction and administrative accountability. It is not enough to simply destroy the data; an organization must also be able to prove, at any given moment, exactly how and when that destruction occurred. This demand for transparency is driven by both internal security needs and external regulatory requirements, such as those mandated by global data protection acts. As hardware refreshes become more frequent due to rapid technological advancements, the volume of outgoing equipment increases the likelihood of human error or logistical oversight. Establishing a formal partnership with a certified disposition vendor helps mitigate these risks by providing a predictable and secure pipeline for all end-of-life assets, regardless of their physical location or type.
Maintaining Accountability Through Chain of Custody
Effective IT Asset Disposition is as much a logistical challenge as it is a technical one, particularly during large-scale hardware refreshes involving hundreds of endpoints. The risk of a data breach is perhaps highest during the transit phase, where devices are moved from a secure office environment to a processing facility. Without a strict chain of custody, a single lost laptop can translate into a multimillion-dollar liability. Professional ITAD providers mitigate this risk by utilizing tracked transportation and maintaining a continuous log of every asset’s movement. This level of accountability ensures that each serial number is accounted for from the moment it is decommissioned until the data is verified as destroyed. By treating the physical transport of retired hardware with the same urgency as a high-security courier service, businesses can eliminate the black hole period where assets often go missing, thereby closing a major gap in their defensive posture.
Establishing Evidence with Certificates of Destruction
The ultimate defense against regulatory scrutiny and potential litigation lies in the administrative documentation generated during the disposal process. A Certificate of Destruction serves as the definitive proof that an organization has fulfilled its legal and ethical obligations to protect sensitive data. In 2026, simply claiming that data was erased is no longer sufficient; auditors and partners require a verifiable, searchable record for every individual device that has exited the fleet. These certificates provide a clear audit trail that links specific hardware to recognized sanitization methods, such as shredding or multi-pass wiping. Having this information readily available in a centralized digital database allows an organization to respond to inquiries within minutes rather than days. This administrative rigor transforms ITAD from a backroom chore into a core pillar of corporate governance, ensuring that the retirement of hardware is a transparent and defensible event.
Evaluating Your Current Security Posture
To ensure that these risks were properly managed, proactive organizations implemented a simple yet effective litmus test for their disposal protocols. Leadership reviewed any device retired within the previous six months and attempted to answer three critical questions regarding its status. They sought to confirm the exact physical location of the asset and verified the existence of a specific document proving the data was destroyed according to NIST standards. Furthermore, they tested whether this documentation was immediately accessible to an auditor without the need for extensive research. When these questions were answered with certainty, the organization demonstrated a mature and robust security posture. Conversely, the inability to provide this proof highlighted a non-hypothetical gap that required immediate remediation. By formalizing the disposal process, businesses moved beyond a reliance on luck and established a sustainable, defensible framework for hardware retirement that protected their reputation.