
Editorial
When data is lost, stolen, or mishandled, the consequences no longer stop at a fine or a news cycle. For industrial and B2B organizations, where physical assets and digital systems are increasingly intertwined, a breach can mean disrupted infrastructure, regulatory penalties, damaged partnerships, and reputational harm that takes years to recover
A data breach in 2026 is more than an IT incident; it is a business crisis. Regulatory penalties, reputational damage, and the loss of customer trust that come from it can take years to recover from, and the financial consequence is high. According to IBM’s 2026 Cost of a Data Breach Report, the global average breach cost is $4.99 million, a 12%
According to IBM, the average cost of a data breach reached $4.88 million in 2024 , and that figure may not capture all the customer churn, regulatory penalties, and reputational damage that can follow. For business leaders, customer data protection is an operational responsibility that directly affects trust, revenue, and business continuity.
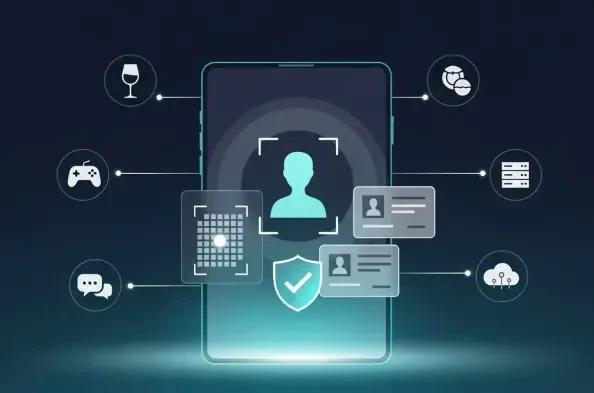
Age verification is gaining momentum across many industries and has become a major compliance challenge, particularly for corporations managing sensitive customer data through a data protection center. Once limited to sectors such as gambling, alcohol sales, and tobacco, it is now expanding into social media, online marketplaces, adult content
A customer updates a profile, submits payment details, or opens a support ticket, assuming the company will handle that information responsibly. Internally, that same information flows through applications, analytics tools, customer relationship systems, support platforms, and third parties. One weak access rule, one misrouted file, or one
Cloud risk has become a direct financial, reputational, and regulatory concern for executive teams. As enterprises run increasingly complex multi-cloud and multi-SaaS portfolios, the attack surface now spans identities, integrations, and data pipelines that most security teams lack full visibility into. Data moves constantly across SaaS platforms,