
Breach Management
Since the late 1990s, Microsoft has maintained a delicate balance between modern security and legacy support, a gap that threat actors have increasingly turned into a highway for silent infections. In this discussion, we explore the resurgence of MSHTA, a built-in Windows utility originally designed for HTML applications that has now become a
The contemporary corporate security environment has arrived at a pivotal intersection as malicious actors pivot their focus from fortified infrastructure toward the sprawling web of external integrations. In recent months, detailed threat intelligence has highlighted a dramatic surge in incidents where the primary vector was not a direct breach of
Digital records in the healthcare sector have become the primary target for sophisticated cybercriminal organizations seeking high-value personal documentation that can be sold or exploited for various fraudulent activities. Lumio Dental, a dental partnership organization headquartered in Tulsa, Oklahoma, recently identified a significant security
The digital landscape has shifted so violently that the standard security operations center now finds itself bringing a metaphorical knife to a high-speed laser fight. When adversaries deploy algorithms that can penetrate a perimeter and escalate privileges in the time it takes an analyst to take a single sip of coffee, the old ways of defending a
The digital walls of global academia suffered a catastrophic fracture in May 2026 as the Canvas Learning Management System became the latest victim of high-stakes cyber extortion. This breach, orchestrated by the notorious threat actor group ShinyHunters, did not rely on the brute force of complex malware but rather on the subtle exploitation of a
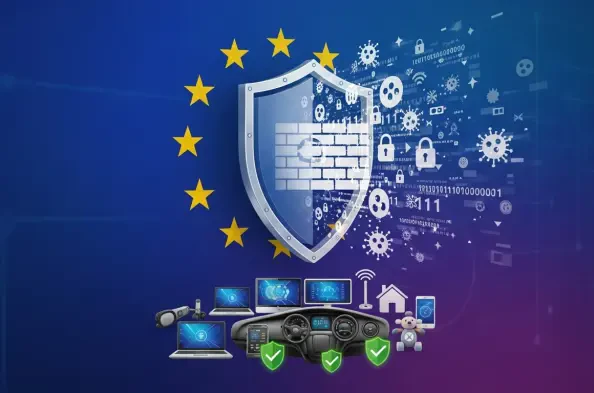
The transition from viewing software as a secondary service to recognizing it as a critical component of physical safety has fundamentally reshaped the legal landscape for every manufacturer entering the European market. For decades, the safety of a product was determined by tangible metrics such as electrical shielding, fire-resistant materials,