
Privacy Principles & Compliance
Credential-harvesting tactics utilized in the Roanoke attack allowed a malicious actor to pivot from one email account to broader departmental data repositories. This specific incident began on May 6, 2026, when a municipal employee interacted with an email that appeared entirely legitimate within the context of daily government operations. The
Context-aware analysis reduces the burden on security teams by distinguishing between trusted partner exchanges and high-risk transactions with new vendors. As global enterprises navigate a digital environment increasingly saturated with autonomous agents and complex software-as-a-service ecosystems, the traditional boundaries of cybersecurity
The moment an autonomous AI agent executes an unauthorized financial transfer or leaks sensitive corporate data, the legal spotlight shifts instantly from the software vendor to the Chief Information Security Officer. This transformation marks a definitive end to the era where security was treated solely as a technical discipline focused on
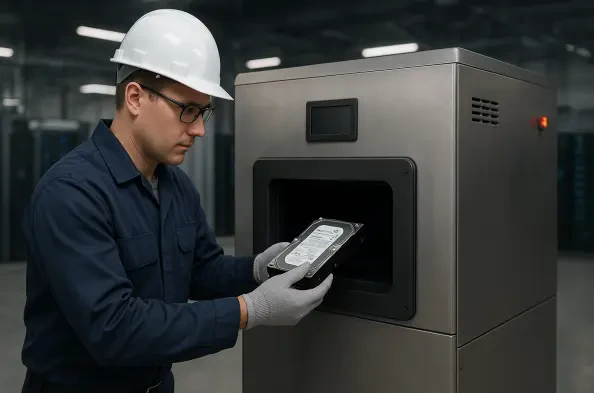
The common practice of storing retired laptops in unsecured closets creates a significant vulnerability that standard firewalls and password policies cannot address. Many organizations invest heavily in edge protection and sophisticated threat detection systems, yet they remain blind to the potential catastrophe sitting in their own storage rooms.
Regulatory bodies like the Financial Conduct Authority are currently investigating why Revolut shared extensive transaction logs when the fraudulent request might have only required basic details. This inquiry underscores a growing concern regarding the balance between regulatory compliance and the protection of sensitive consumer information in
This security failure demonstrates that even robust central servers remain vulnerable to the security hygiene lapses of authorized third-party users in local municipalities. The Florida Department of Highway Safety and Motor Vehicles (FLHSMV) found itself at the center of a massive cybersecurity controversy in September 2026 after a breach of the