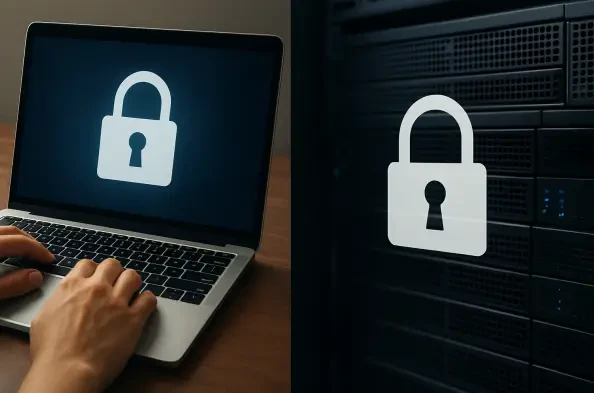
In a server-side encryption model, data is usually transmitted via an encrypted tunnel like HTTPS before being locked away using keys controlled by the service provider. This approach has dominated the digital landscape for years because it offers a seamless user experience where the provider manages all the technical heavy lifting, including key rotation and storage redundancy. However, as the digital ecosystem of 2026 matures, the debate over data sovereignty has shifted focus toward the location of the encryption key rather than just the strength of the algorithm itself. While the Advanced Encryption Standard (AES-256) remains the gold standard for securing data at rest, the distinction between who holds the key defines the fundamental relationship between a user and their digital information. When a service provider manages the keys, they effectively act as a custodian of the user’s secrets, a model that prioritizes accessibility and recoverability over absolute confidentiality. Conversely, moving the encryption process to the local device fundamentally alters the threat model by ensuring that the plaintext never leaves the user’s physical control. This architectural choice necessitates a deeper look at the cryptographic underpinnings that allow these systems to function while balancing the demands of modern cloud-based computing and personal privacy.
Technical Foundations: Symmetric and Asymmetric Methodologies
The underlying mechanics of any secure system rely on a sophisticated interplay between symmetric and asymmetric cryptography. Symmetric encryption, represented most famously by the Advanced Encryption Standard, is prized for its computational efficiency and speed, making it the ideal choice for encrypting large datasets or entire hard drives. In this scenario, the same mathematical key is used for both the locking and unlocking processes, requiring a secure method to share that key between authorized parties. This performance efficiency is why nearly all encryption at rest solutions utilize symmetric algorithms for the heavy lifting. However, the challenge of securely distributing these keys led to the widespread adoption of asymmetric encryption, such as Elliptic Curve Cryptography (ECC) or RSA. Asymmetric systems use a mathematically linked key pair, consisting of a public key that can be shared openly and a private key that remains strictly confidential. This allows users to establish secure communication channels and exchange symmetric keys without ever revealing the secret credentials to potential eavesdroppers. In 2026, the integration of these two methods has become seamless, forming a hybrid approach that provides both the speed necessary for high-volume data transfers and the rigorous security required for modern digital identity management.
To conceptualize how these mathematical principles manifest in real-world services, one can envision a standard courier service handling a sensitive document. In a server-side model, the user hands an open letter to the courier, who then places it inside a heavy-duty company safe at the central warehouse. The user trusts the courier to keep the letter private, but the courier technically possesses the master key to that safe and could, under specific circumstances, access the contents. This represents the trade-off inherent in most modern cloud infrastructures where the provider offers robust security against external threats but remains an internal gatekeeper. In contrast, client-side encryption is akin to the user placing the letter inside their own personal, unpickable safe before the courier ever arrives. The courier still moves the safe from the point of origin to the destination, but at no point during transit or storage does the courier have the capability to peek inside. Even if the courier’s warehouse is compromised by a sophisticated heist, the thieves would find a collection of locked safes that are useless without the keys held exclusively by the individual owners. This analogy highlights that the central point of contention in modern data security is not the strength of the lock, but rather the physical and digital location of the person holding the key.
Architectural Realities: The Client-Side Security Model
Client-side encryption, often synonymous with zero-knowledge architecture, dictates that the encryption process occurs entirely on the user’s local hardware before any information reaches the internet. In this workflow, the application generates a unique cryptographic key locally, uses it to scramble the data into ciphertext, and only then transmits the unreadable package to the service provider’s infrastructure. This ensures that the provider acts purely as a dumb storage medium, holding blobs of data that it cannot interpret or index. This model has become the standard for privacy-centric tools like Signal and Proton, as well as for the management of non-custodial cryptocurrency wallets where the user’s seed phrase is never shared with a central server. By moving the security perimeter to the individual device, developers can offer a guarantee of privacy that is mathematically provable, as the provider physically lacks the keys required to comply with data requests or internal audits. This shift to the edge of the network reflects a growing trend in 2026 where users demand absolute control over their sensitive information, forcing service providers to adopt architectures that limit their own liability and access to personal data while maintaining a reliable service.
Despite the undeniable privacy benefits, the implementation of client-side encryption introduces a heavy operational burden on the user and limits the overall functionality of the application. Because the service provider cannot read the stored data, they are unable to provide standard cloud features such as server-side search, content indexing, or automatic file previews. For instance, a user searching through a massive archive of client-side encrypted documents would have to download and decrypt the entire database locally to perform a simple keyword search, which is often prohibitively slow for large-scale enterprise use. Furthermore, the zero-knowledge nature of this model means that if a user loses their private key or forgets their master password, there is no forgot password link that can restore access. The service provider cannot assist in data recovery because they never possessed the credentials to begin with, leading to scenarios where a single lost device or forgotten phrase results in the permanent loss of vital information. This creates a high-stakes environment where the user must take full responsibility for their own key management and backup strategies, a requirement that often keeps client-side encryption limited to specialized niches or highly technical user bases who prioritize absolute security over day-to-day convenience.
Operational Dynamics: The Server-Side Protection Standard
Server-side encryption remains the dominant choice for the majority of consumer and enterprise cloud applications due to its inherent flexibility and ease of use. In this model, data is transmitted to the server through an encrypted tunnel, such as Transport Layer Security (TLS), and is then encrypted by the service provider’s own systems before being committed to persistent storage. This protection at rest guards the data from physical theft of hardware and unauthorized access by lower-level infrastructure personnel. Since the service provider manages the keys, they can offer a suite of advanced features that enhance the user experience, such as real-time collaboration, sophisticated search algorithms that scan through millions of documents in milliseconds, and the ability to recover accounts for users who have lost their credentials. This approach allows mainstream platforms like Google Workspace or Amazon S3 to provide high-performance environments where security is handled transparently in the background, requiring no specialized knowledge or technical management from the end-user. In the competitive landscape of 2026, this frictionless experience is often the deciding factor for organizations that need to balance rigorous data protection with the practical requirements of a global workforce.
However, the centralization of key management in a server-side model introduces a different set of risks that must be carefully managed by both the provider and the user. Because the service provider holds the master keys, they possess the technical ability to decrypt any user data at will, creating a single point of failure that could be targeted by advanced persistent threats or compromised by internal actors. Furthermore, this architecture makes the provider a primary target for legal subpoenas and government surveillance requests, as the provider can be legally compelled to turn over decrypted information. While reputable companies implement strict internal controls and multi-party authorization protocols to prevent unauthorized key access, the fundamental reality remains that the user is relying on the provider’s integrity and security posture rather than mathematical certainty. This reliance on a trusted third party represents a significant vulnerability in the context of high-stakes corporate espionage or targeted state-sponsored cyberattacks. Consequently, while server-side encryption fulfills the basic regulatory requirements for many industries, it often falls short of the privacy required for the most sensitive legal, medical, or financial communications that demand a truly decentralized security approach.
Strategic Integration: Hybrid Techniques and Envelope Encryption
To address the performance bottlenecks and security gaps of traditional models, modern cloud architects in 2026 have increasingly turned to a sophisticated method known as envelope encryption. This technique bridges the gap between client-side and server-side logic by utilizing a layered approach to key management. In an envelope encryption workflow, the system generates a unique, one-time data key for every individual file or data object. This data key is used to encrypt the content using a high-speed symmetric algorithm, ensuring that the actual encryption process remains fast and scalable. Once the file is encrypted, the data key itself is then encrypted using a much more secure master key that is stored in a dedicated Hardware Security Module (HSM) or a specialized key management service. The resulting wrapped data key is stored alongside the encrypted file. To access the data, the system must first request the master key to unwrap the data key, which then unlocks the original content. This multi-layered structure allows organizations to maintain centralized control over a few high-level master keys while distributing the encryption of millions of individual files, significantly reducing the blast radius of a potential key compromise and enhancing overall system resilience.
The choice between implementing client-side or server-side encryption ultimately hinges on the specific value proposition of the application and the level of risk the user is willing to accept. For products where privacy and anonymity are the core features, client-side encryption is the only viable path to establishing a relationship of absolute trust. It signals to the user that the developer is technically incapable of viewing their data, which is essential for password managers, medical record systems, and investigative journalism tools. On the other hand, for general-purpose tools where collaboration, speed, and recovery are paramount, server-side encryption offers a pragmatic balance that meets the needs of the vast majority of users. Decision-makers must evaluate whether their target audience values the safety net of a managed service or the ironclad autonomy of a zero-knowledge system. This strategic alignment ensures that the chosen security architecture supports the broader goals of the platform, whether that involves facilitating global teamwork in a corporate setting or providing a sanctuary for private digital expression in an increasingly transparent world. In 2026, the maturity of these technologies allows for a more nuanced implementation that can even offer tiered security levels based on the sensitivity of the specific data being handled.
Strategic Path Forward: Lessons From Architectural Evolution
The historical evolution of encryption architectures led to a consensus that neither method was inherently superior, but rather served distinct operational objectives. It was observed that organizations which prioritized user convenience through server-side models successfully maintained high adoption rates, as the lack of technical friction allowed for rapid scaling and complex data processing. These systems provided essential features like full-text search and account recovery that many users considered non-negotiable for their daily digital activities. At the same time, the rise of high-profile data breaches and increasing awareness of digital surveillance pushed a significant segment of the market toward client-side alternatives. Those who adopted zero-knowledge frameworks effectively mitigated the risks associated with central server compromises, ensuring that the impact of a security incident was limited to the provider’s infrastructure rather than the integrity of the user’s private information. This divergence in strategy established a clear roadmap for developers, who began to categorize data based on its trust requirement before selecting an encryption path, leading to more resilient and specialized digital services across the industry.
Moving forward, the industry successfully transitioned into a model where the key ownership question became the primary design consideration for every new project. It was determined that a tiered approach, combining the accessibility of server-side encryption for non-sensitive data with the rigorous privacy of client-side encryption for highly personal information, offered the most sustainable path for long-term data management. Professional teams began to implement envelope encryption as a baseline standard for cloud storage, while simultaneously offering opt-in client-side modules for specific folders or communication channels. This strategic flexibility allowed platforms to meet diverse user needs while maintaining compliance with international data protection laws that demanded varying levels of security for different types of personal information. The lessons learned from this period underscored the importance of transparency in security architecture, as users became more adept at distinguishing between basic encryption and absolute privacy. By prioritizing clear communication regarding key management protocols, providers built stronger foundations of trust with their audiences, ultimately resulting in a more secure and functional digital ecosystem that respected the balance between individual autonomy and collective utility.