
Third-Party Risk Management
Treating sovereignty as a mere regulatory checkbox prevents many organizations from addressing the long-term risks of technological dependency. Modern enterprises often find themselves trapped between the urgent need for digital transformation and the complex web of global data regulations that dictate where information must reside. Although
The rise of shadow AI mimics the previous decade's shadow IT crisis, with employees increasingly utilizing unapproved tools that inadvertently expose sensitive proprietary data to external servers. This unchecked proliferation signals a broader AI hangover, where the initial excitement surrounding rapid deployment has given way to the complex
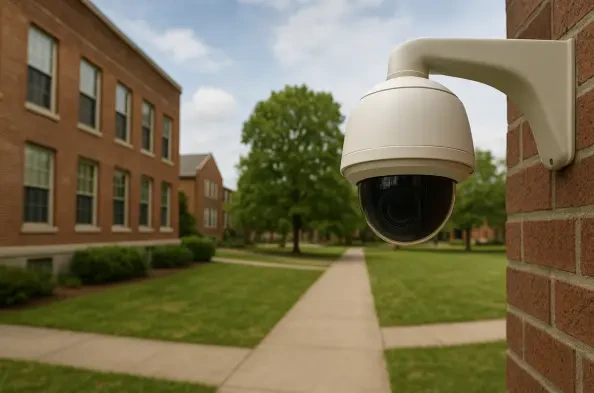
University officials have acknowledged that Texas Senate Bill 4 prevents them from guaranteeing that license plate data will not be shared with federal immigration authorities. Since 2022, the University of Texas at Dallas has utilized the Flock Safety automatic license plate recognition system to monitor vehicle traffic entering the campus
The quiet corridors of global artificial intelligence laboratories currently echo with a debate centering on whether a voluntary safety protocol represents a genuine shield or merely a piece of corporate architecture designed to deflect regulation. While OpenAI publicly advocates for rigorous safety standards, its latest framework for third-party
Digital infrastructure usually thrives on the promise of perpetual uptime, yet a sudden mandate to sever all connectivity recently sent shockwaves through the global cybersecurity community. The directive arrived on September 25 with a jarring finality, instructing organizations to paralyze their digital lifelines to avoid a potentially
Open-source software libraries have become a central focus of the initiative because much of the world's digital infrastructure is built on shared, potentially vulnerable code. This reality has prompted the federal government to establish a robust framework capable of defending the digital frontier against increasingly sophisticated threats. The