
Third-Party Risk Management
The systemic stability of the modern global economy now hinges on a few lines of code stored within remote data centers that most corporate leaders will never physically visit. When a single authentication error in a legacy server can paralyze the operations of thousands of global corporations, the cloud starts to look less like a resilient
The moment an autonomous AI agent executes an unauthorized financial transfer or leaks sensitive corporate data, the legal spotlight shifts instantly from the software vendor to the Chief Information Security Officer. This transformation marks a definitive end to the era where security was treated solely as a technical discipline focused on
Corporate boards often find themselves paralyzed during a ransomware attack because technical security data fails to translate into clear business risks. When a massive intrusion occurs, the immediate fallout involves a frantic rush by IT departments to identify the source and scope of the breach, yet the information they relay to the boardroom is
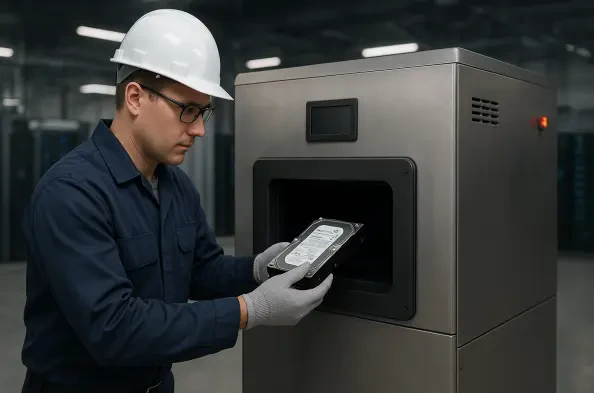
The common practice of storing retired laptops in unsecured closets creates a significant vulnerability that standard firewalls and password policies cannot address. Many organizations invest heavily in edge protection and sophisticated threat detection systems, yet they remain blind to the potential catastrophe sitting in their own storage rooms.
Agentless side-scanning technology has revolutionized estate-wide visibility by allowing security teams to discover vulnerabilities and data exposures in minutes without deploying sensors. This shift has fundamentally changed how organizations approach the security of their diverse environments, moving away from fragmented tools toward a unified
This security failure demonstrates that even robust central servers remain vulnerable to the security hygiene lapses of authorized third-party users in local municipalities. The Florida Department of Highway Safety and Motor Vehicles (FLHSMV) found itself at the center of a massive cybersecurity controversy in September 2026 after a breach of the