
Third-Party Risk Management
Medicaid recipients in Kentucky were left in a period of extended vulnerability as the detection gap for the intrusion stretched from late March until mid-August. This security failure, centered on the KY Health-Net Provider Portal, exposed the fragile architecture of public health data management where government efficiency often relies on
The reliance on a handful of global chip suppliers creates a systemic risk where a single architectural flaw could compromise millions of vehicles across different brands. As the automotive industry shifts from mechanical manufacturing to a software-centric model, cars have become sophisticated mobile ecosystems that are deeply integrated with
The modern managed service provider (MSP) landscape has shifted from manual maintenance to automated, high-velocity data protection frameworks where a single configuration error can jeopardize thousands of endpoints simultaneously. ConnectWise Cloud Backup serves as a cornerstone of this ecosystem, providing a direct bridge between complex
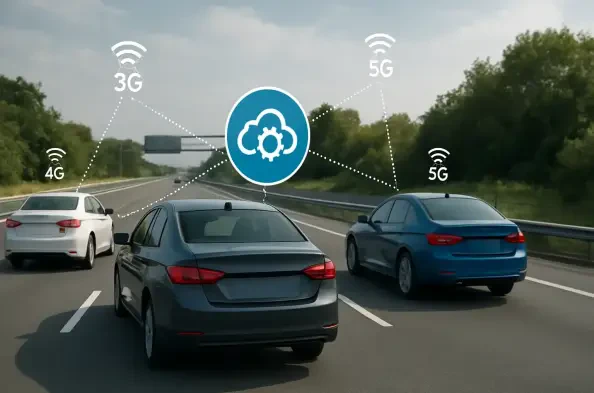
The automotive industry has reached a critical tipping point where digital security is now considered as essential as physical crash safety standards. As passenger cars evolve from mechanical machines into sophisticated rolling computers, the integration of wireless communications, telematics, and high-definition sensors has fundamentally altered
The discovery of an unencrypted plaintext archive containing over one million billing records proved to be a critical aggravating factor during the two-year investigation into BCHP’s security practices. This massive lapse in basic digital hygiene transformed a standard cybersecurity inquiry into a multi-million dollar enforcement action that
Building critical business infrastructure on third-party models often results in dependency debt when those models do not receive consistent security patches or performance updates. This has become increasingly prevalent as enterprises move away from centralized API solutions toward autonomous deployments using weights downloaded from public